Governments love shiny red phones. During the Cold War, Washington and Moscow relied on a direct teletype link to prevent accidental nuclear annihilation. It felt tangible. It felt like control.
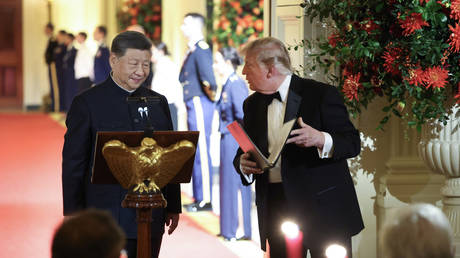
Now, policymakers are applying that exact nineteenth-century logic to twenty-first-century algorithmic systems. The announcement that the United States and China have established a diplomatic channel for artificial intelligence incidents is being hailed as a diplomatic triumph. Bureaucrats are popping champagne in Geneva and Brussels. Think tanks are publishing breathless reports about risk mitigation and safety guardrails. For another perspective, check out: this related article.
It is complete nonsense.
I have watched policy committees burn millions of dollars drafting bureaucratic frameworks for technologies they barely comprehend. I have sat in rooms where senior defense officials nod gravely at concepts they treat as mere buzzwords. This hotline is not a shield against catastrophe. It is political theater designed to soothe panicked markets and give politicians a clean photo-op. Similar reporting on this matter has been published by CNET.
Algorithms do not wait for translation services. They do not care about diplomatic niceties, face-saving communiqués, or midnight phone calls between ambassadors. When a high-frequency trading model or an autonomous defense grid misinterprets a signal, the timescale of failure is measured in milliseconds, not hours. By the time a bureaucrat in Washington picks up the secure line to call Beijing, the economic damage is done, or the escalation spiral has already locked in its devastating trajectory.
To understand why this bilateral agreement is a structural failure, you have to look at how modern machine learning systems actually fail in the wild.
Most politicians imagine an artificial intelligence disaster as a rogue terminal screen flashing red in a secure bunker, giving humans thirty minutes to negotiate an off-switch. That is Hollywood fiction. Real algorithmic failures are silent, distributed, and emergent. They happen when interconnected models interact across borders, sharing data streams, feedback loops, and optimization goals that no single human engineer fully maps out or anticipates.
Imagine a scenario where an automated logistics optimization model used by a major multinational supply chain misinterprets a minor tariff adjustment by a rival superpower. The model begins aggressively rerouting critical materials, predicting a scarcity that does not exist in reality. Autonomous trading algorithms on both sides detect the anomalous supply chain shifts and trigger automated sell-offs. Within four minutes, billions of dollars in market value evaporate, and critical infrastructure inputs are starved of essential resources.
Where does the hotline fit into that timeline? Does an undersecretary call a counterpart to say, "Hey, our neural network hallucinated a trade war"?
The lazy consensus among international relations scholars is that communication prevents escalation. That rule works when two rational human leaders are misinterpreting each other's military exercises. It fails entirely when the actors driving the crisis are lines of compiled code running on tens of thousands of specialized processors across decentralized server clusters. You cannot negotiate with a loss function.
Why did both superpowers agree to this initiative if it is functionally useless? Follow the incentives.
For the United States national security apparatus, establishing a hotline proves to domestic critics and nervous allies that officials are doing something proactive about technological risk without requiring any painful legislative concessions or domestic silicon export halts. It provides an easy headline. It signals competence where none has been tested.
For Beijing, signing onto an incident management channel costs nothing while conferring equal status as a co-manager of global technical stability. It validates China's position as an equal superpower peer in shaping international norms and diplomatic protocols.
Neither side actually intends to use this channel for fast-moving technical emergencies. Instead, it will become a dumping ground for diplomatic protest notes, finger-pointing over cyber espionage, and performative posturing. When a real incident occurs, the hotline will sit quiet because neither capital will trust the other not to exploit the admission of a software failure for intelligence or propaganda advantage.
I have seen companies blow millions on internal compliance committees that exist solely to generate paper trails, proving liability is shared rather than fixing the underlying architectural flaws. This bilateral agreement is the geopolitical equivalent of those compliance committees. It is insurance against blame, not insurance against risk.
If diplomatic hotlines are useless, what actually works? How do we prevent catastrophic algorithmic misalignments between rival nations?
We need to abandon the fantasy of human-in-the-loop crisis management and move toward cryptographic verification and automated circuit breakers at the hardware layer.
First, we need technical mandates built directly into advanced computing infrastructure. Instead of relying on politicians to talk each other down after an incident, we should implement hardware-enforced rate limits and transparent audit trails that operate independently of state software. If an advanced model begins exhibiting anomalous scaling behavior or rapid cross-border data extraction, automated containment protocols should trigger instantly at the chip level, freezing execution before human operators even notice the anomaly.
Second, we must separate technical safety standards from political negotiations. Diplomatic channels are inherently corruptible by geopolitical tension. If relations sour over unrelated territorial disputes, the hotline becomes a weaponized tool of non-cooperation. Safety mechanisms must be governed by independent, technical verification bodies—similar to how international aviation standards operate—where engineers from both nations verify protocols based on mathematics rather than political posturing.
Third, stop pretending that transparency means sharing source code or proprietary weights. That is a non-starter for both national security agencies and commercial entities. True technical transparency means verifiable safety proofs, zero-knowledge proofs of model constraints, and standardized stress-testing methodologies that can be executed in sandbox environments without exposing classified architectures.
The uncomfortable reality that nobody in the foreign policy establishment wants to admit is that artificial intelligence development is not a game of cooperative chess. It is an intense, zero-sum race for economic and military dominance.
Pretending that a hotline can smooth over structural competition is like putting a seatbelt on a rocket ship and calling it an airplane. The interests of Washington and Beijing are fundamentally misaligned when it comes to technological supremacy. Every breakthrough in automation shifts the balance of power. Every defensive measure looks like an offensive threat to the other side.
When you rely on diplomatic quick fixes, you create a false sense of security. Leaders sleep better at night believing a safety net exists, which only encourages them to push technical boundaries faster and harder, assuming the hotline will catch them if they fall. That moral hazard is far more dangerous than the raw technology itself.
Stop celebrating symbolic communication channels. Stop trusting politicians to manage code they cannot write. If we do not replace bureaucratic theater with rigorous, automated, hardware-enforced safeguards, our digital future will be written by algorithms operating at speeds we cannot comprehend, monitored by leaders who chose a red phone over reality.